Installation
Agent Harbor runs on macOS, Linux, and Windows.
Quick Install (Recommended)
The easiest way to install Agent Harbor on macOS, Linux, or WSL is using our install script:
curl -fsSL https://install.agent-harbor.com | bashOr on Windows (PowerShell):
irm https://install.agent-harbor.com/windows | iexOr with a GitHub token for private repository access:
curl -fsSL https://install.agent-harbor.com | GITHUB_TOKEN=xxx bashThis script will:
- Detect your OS and CPU architecture (or install Nix package manager if needed)
- Configure the signed binary repository / Cachix binary cache for fast downloads
- Install the Agent Harbor CLI (
ah)
Install via Nix
Prerequisites
- Nix with flake support enabled
Install Nix
If you don’t have Nix installed:
curl -L https://nixos.org/nix/install | shAfter installation, enable flake support by adding to ~/.config/nix/nix.conf:
experimental-features = nix-command flakesInstall Agent Harbor
nix profile install github:agent-harbor/agent-harborLinux, macOS & Windows Packages
Native packages are available for Debian/Ubuntu (APT), Fedora/RHEL (YUM/DNF), macOS (Homebrew), and Windows (Scoop / Winget).
Debian / Ubuntu (APT)
# Import the GPG signing key
curl -fsSL https://apt.agent-harbor.com/gpg-key.asc | sudo gpg --dearmor -o /etc/apt/keyrings/agent-harbor.gpg

# Add the repository
echo "deb [signed-by=/etc/apt/keyrings/agent-harbor.gpg] https://apt.agent-harbor.com stable main" | \
  sudo tee /etc/apt/sources.list.d/agent-harbor.list

# Install
sudo apt update && sudo apt install agent-harbor
Fedora / RHEL (YUM/DNF)
# Import the GPG signing key
sudo rpm --import https://yum.agent-harbor.com/gpg-key.asc

# Add the repository
sudo curl -fsSL https://yum.agent-harbor.com/agent-harbor.repo -o /etc/yum.repos.d/agent-harbor.repo

# Install
sudo dnf install agent-harbor
macOS (Homebrew)
brew tap metacraft-labs/metacraft
brew install agent-harbor
Windows (Scoop & Winget)
# Scoop
scoop bucket add metacraft https://github.com/metacraft-labs/metacraft-desktop-packages
scoop install metacraft/agent-harbor

# Winget
winget install AgentHarbor.AgentHarbor
GPG Signing Key
All Linux packages are signed with our GPG key. You can verify the key fingerprint:
| Property | Value |
|---|---|
| Fingerprint | 49A0 5F0A 96A8 38FA 15CA 2783 1E12 51FF 0C8C D19D |
| Key ID | 1E1251FF0C8CD19D |
[email protected] | |
| Type | RSA 4096-bit |
To verify the key after importing:
gpg --show-keys /etc/apt/keyrings/agent-harbor.gpg
# Or for YUM:
rpm -qa gpg-pubkey --qf '%{NAME}-%{VERSION}-%{RELEASE}\t%{SUMMARY}\n' | grep -i harbor
Building from Source
Prerequisites
- Nix with flake support (provides all build dependencies)
- Git
Clone and Build
git clone https://github.com/agent-harbor/agent-harbor.git
cd agent-harbor
direnv allow  # or: nix develop
cargo build --bin ah
The binary will be at ./target/debug/ah (or under $CARGO_TARGET_DIR if set).
For a release build:
cargo build --release --bin ahThe release binary will be at ./target/release/ah (or under $CARGO_TARGET_DIR if set).
Verify Installation
ah --versionCheck System Health
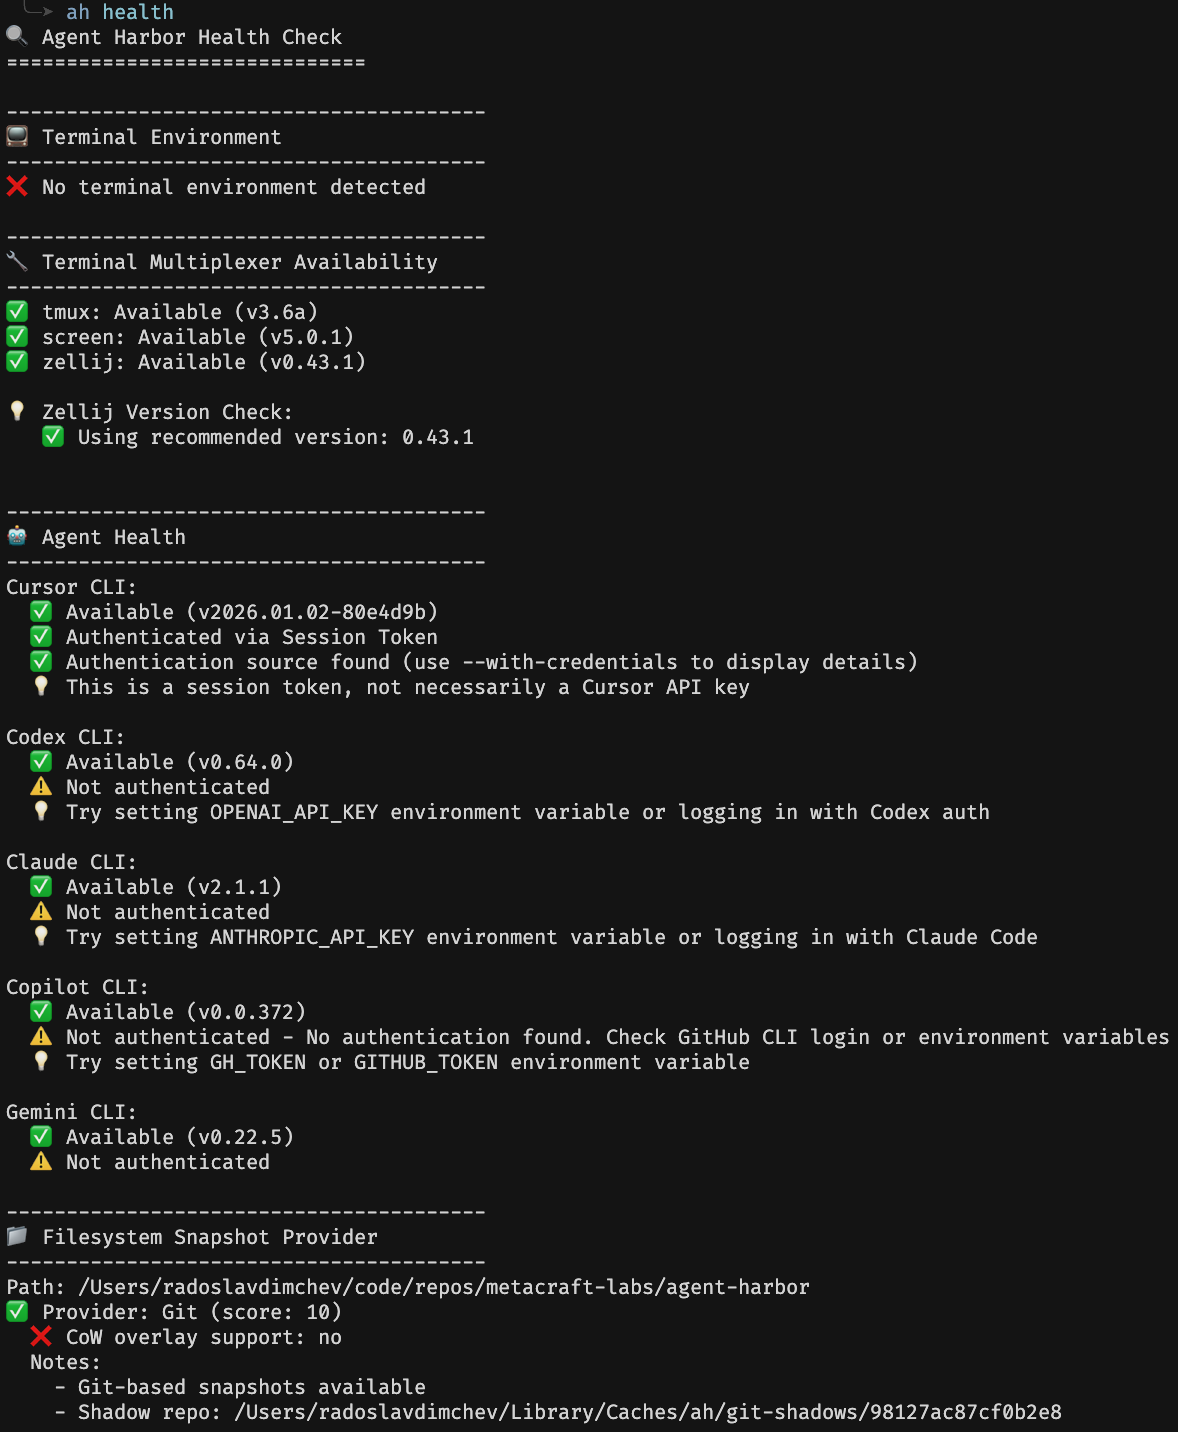
Run the health check to verify your setup:
ah healthThis checks:
- Agent availability and credentials
- Filesystem snapshot provider support
- Terminal multiplexer detection
Agent Credentials & Fleet Login
Agent Harbor uses each agent’s native credential system and can also synchronize credentials across your fleet via ah login and ah credentials. Before using an agent, authenticate with it directly or import it:
Claude Code
claude
# Follow the authentication prompts
OpenAI Codex
codex authImport or Manage Credentials via Agent Harbor
# Optional: sign in to agent-harbor.com (or --server <url>) to sync encrypted credentials
ah login

# Import existing host logins into the Agent Harbor credential registry
ah credentials import claude
ah credentials import codex
Verify Credentials
ah healthThe health check will show which agents have valid credentials configured.